Skip to content

Services

Your IoT data, secure by design

A secure IoT data platform means your telemetry is protected at every step — encrypted on the way in, encrypted at rest, reachable only by the people and systems you authorise, and logged so you can see who did what and when. We design the platform around that principle rather than bolting security on afterwards: data is separated site by site and client by client, every device has its own identity, and access is role-based and least-privilege by default. The result is a platform you can put in front of an auditor, a board or a regulator with confidence — built and supported in the UK by the same team that engineers the devices feeding it.

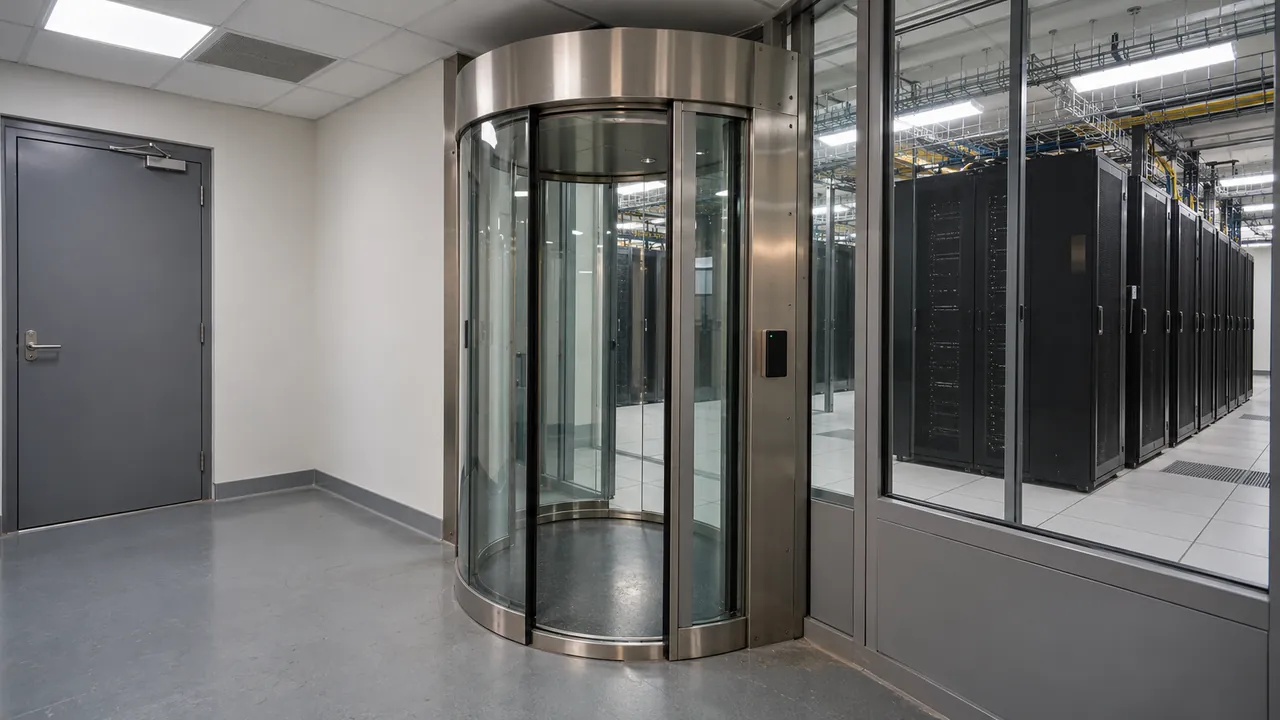
Illustrative photo of a glass security airlock leading to a data hall of server racks, the kind of controlled environment behind secure IoT data platforms
Encrypted
Telemetry protected in transit and at rest
Role-based
Least-privilege access by default
Audited
Every meaningful action logged and traceable
UK
Built and supported in the UK
01

Security designed in, not bolted on

Security on an IoT platform cannot be an afterthought, because the data it carries is often the basis for safety, compliance and operational decisions. We design for it from the start. The same UK team that engineers the devices builds the platform that receives, stores and surfaces their data, so security is considered at every layer rather than patched on at the end. That means sensible defaults — encryption on, least-privilege access, logging enabled — rather than options a client has to remember to switch on.

02

Real-time alerts to the right people

Monitoring is only useful if the right person hears about a problem while there is still time to act. Each reading and event is checked against the thresholds set for that sensor as it arrives, and an alert goes out straight away by email, SMS or both, or through an app where the client wants one. Thresholds are set sensor by sensor: a high or low limit, a reading that drifts slowly over several hours, a door left open outside agreed hours, a contact that changes state. On a 4G gateway, an alert reaches the dashboard about a second after the reading arrives.

Alerts go to named people for each site, with escalation to further contacts when the first person does not respond, so an out-of-hours alarm does not sit unread in one inbox. Silence counts as a fault as well. Every tag checks in on a schedule set for the site, so a tag that stops reporting raises its own alert, and gateways carry battery backup, with the platform alerted the moment one loses mains power. Every alert is kept in a timestamped event history, held in the cloud or on the client's own servers, and alerts are never metered or charged per message.
03

Encrypted in transit and at rest

Telemetry is encrypted on its way into the platform and encrypted while it is stored, using industry-standard encryption — TLS in transit, AES at rest. Data is not left in the clear at any point a client would reasonably expect it protected, and the links between systems are secured too. The aim is simple: at no stage between a device in the field and an authorised user's screen is your data casually readable by anyone who should not see it.

04

Access you control, actions you can audit

Access is role-based and least-privilege by default: people and systems see only what their role needs, and nothing more. Permissions are explicit, and changes to them are recorded. Every meaningful action on the platform — a login, a configuration change, an export — is logged, so there is always a clear, timestamped account of who did what and when. When an auditor, a board or a regulator asks how your data is handled, the answer is in the record rather than in someone's memory.

05

Your data, kept separate

In a multi-site, multi-client world, separation matters. Data is held apart site by site and client by client, so one tenant's information is never exposed to another's. Every device carries its own identity, which means telemetry can be trusted to have come from the device it claims to, and a single compromised credential cannot quietly speak for the whole estate. That separation is part of the design, not a configuration a client has to assemble themselves.

06

Resilient, available and supported

A platform is only secure if it is also there when you need it. It is built for high availability and monitored continuously, so problems are seen and dealt with rather than discovered by the client. Telemetry is buffered and reconciled, so a temporary loss of connectivity does not mean lost data — readings come back in order once the link is restored. And because the platform is built and supported by the same UK team that engineers the devices, support is people who understand the whole system, not a first-line script.

07

Built to support your compliance

Many of our clients operate under real compliance obligations — in water, construction, energy, the public sector and beyond. The platform is built to make meeting them easier: encryption, access control, audit logging and data separation are exactly the controls those frameworks expect to see. We work to your specific requirements rather than claim that a single certificate covers every case. If your organisation needs the platform to meet a particular standard, that is a conversation we have openly, with evidence, at the scoping stage.

FAQ

Frequently asked questions

How is IoT data protected on the platform?

Telemetry is encrypted in transit and at rest using industry-standard encryption, access is role-based and least-privilege, and every meaningful action is logged for a full audit trail.

How do real-time alerts reach the right people?

By email, SMS or both, or through an app where required, sent the moment a reading crosses the threshold set for that sensor. Each site has its own named contacts, and an alert escalates to further contacts when the first person does not respond.

Will we know if a sensor or gateway goes offline?

Yes. Tags check in on a schedule set for each site, so a tag that goes quiet raises its own alert instead of being read as all clear. Gateways carry battery backup, and the platform is alerted when one loses mains power.

Who can access our data?

Only the people and systems you authorise. Access is role-based and least-privilege by default, permissions are explicit, and changes to them are recorded.

Is our data kept separate from other clients'?

Yes. Data is separated site by site and client by client, and every device has its own identity, so one tenant's data is never exposed to another and telemetry can be trusted to its source.

Can the platform support our compliance requirements?

Yes. Encryption, access control, audit logging and data separation are the controls most frameworks expect. We work to your specific requirements at the scoping stage rather than assume one certificate fits every case.

What happens to data if connectivity drops?

Telemetry is buffered and reconciled, so a temporary loss of connectivity does not mean lost data — readings are brought back in order once the link is restored.

Make your site signals visible, usable and evidenced.

Tell us about the sites, assets and conditions you need to monitor. We will help scope a practical pilot for reliable telemetry, real-time alerts and evidence-ready reporting.

Location

Venator House, Unit 9, 15-17 St Stephen's Road, Bournemouth

Dorset, BH2 6LA · VAT GB 409644484

Tell us about your enquiry

Provide a few details about your sites, assets and operational needs. We will be in touch to discuss the right approach.

No mailing lists. No spam. We reply directly to your enquiry.